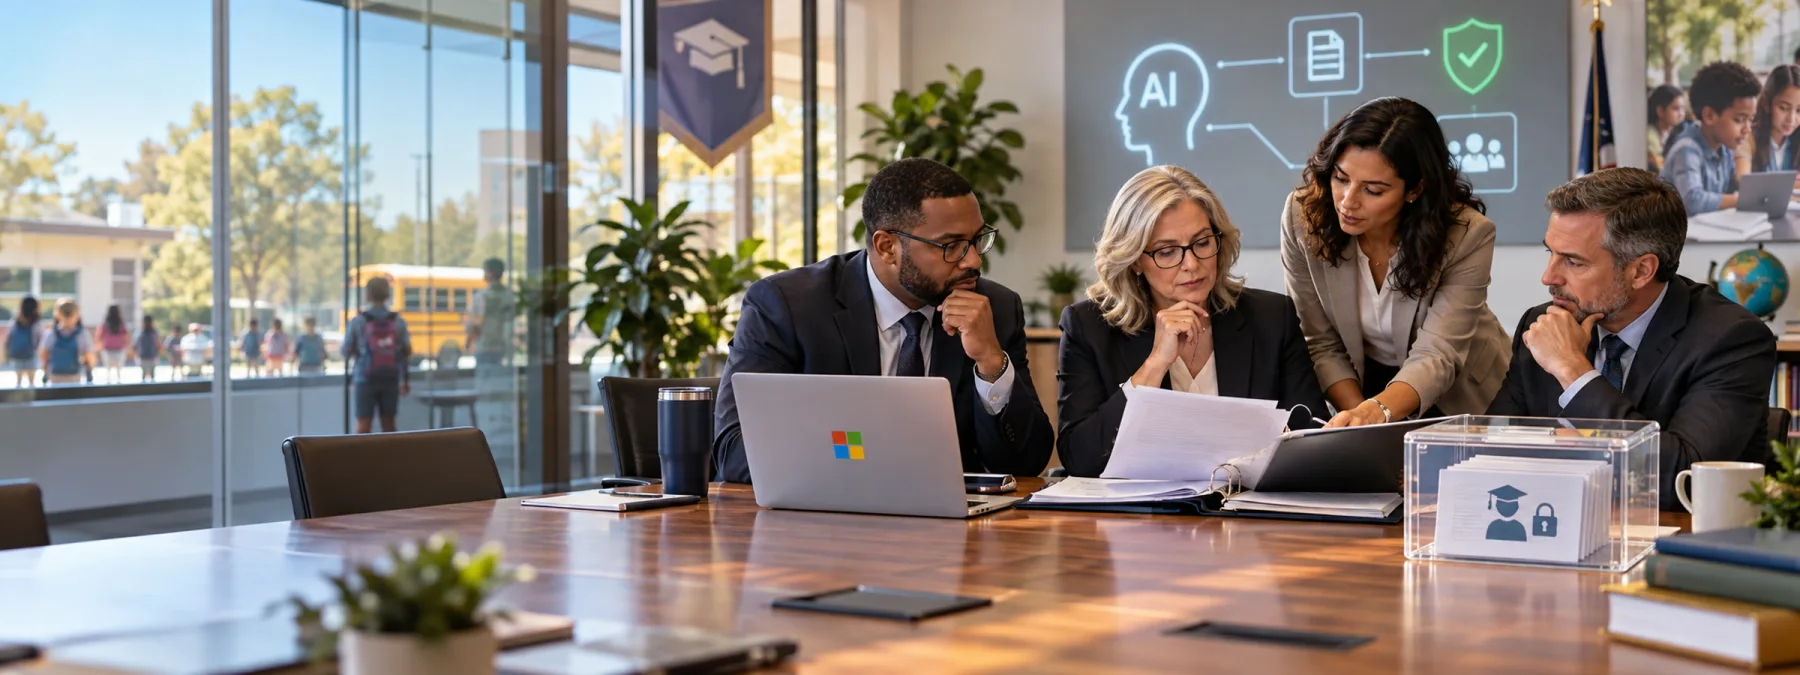
The Associated Press reported today that Microsoft has agreed to a set of AI privacy and safety terms for schools negotiated with the American Federation of Teachers and the United Federation of Teachers. The agreement is notable because it turns a broad AI-in-education debate into contract language: limits on using student and educator data, restrictions on emotionally dependent AI features, third-party audits, and clearer family-facing explanations of how tools work.
For New Jersey schools and other data-sensitive organizations, the important part is not simply that Microsoft made a promise. It is that a large vendor is being asked to put AI privacy expectations into terms that districts can attach to new or existing agreements. That gives school leaders, nonprofits, healthcare practices, and professional services firms a useful model for their own AI vendor reviews.
The contract is where the AI policy becomes real
Many organizations already have an AI policy draft, a staff acceptable-use memo, or a board-level discussion about student data and AI tools. Those documents matter, but they do not control what a vendor can do unless the obligations appear in the agreement, data-processing terms, product documentation, or another enforceable record.
The Microsoft school AI privacy standard, according to the same-day AP report and supporting Microsoft and AFT materials, focuses on practical terms: no use of student or educator data for AI training except limited safety purposes, no sale or advertising use of that data, plain-language transparency for families, human oversight for high-risk decisions, and audit rights. That list is a useful starting point for any organization reviewing AI tools that touch minors, patients, employees, donors, clients, or regulated records.
The business decision is straightforward: should an AI tool be approved because it looks useful, or only after the organization has written answers about data use, retention, deletion, feature changes, and accountability? That is where the homework gets real.
What owners and administrators should ask
Before approving or renewing an AI tool, leaders should ask their IT provider, MSP, software vendor, or internal team a few direct questions:
- What data enters the tool? Identify whether student records, employee information, customer files, medical data, financial records, support tickets, emails, or uploaded documents are included.
- Can the vendor use that data to train or improve AI models? Do not rely on a sales summary. Ask for the contract clause, product setting, or data-processing language.
- How long is the data retained? Retention, deletion, logging, and backup copies should be clear enough for a nontechnical leader to understand.
- Who can review outputs and override decisions? AI should not quietly become the decision-maker for discipline, hiring, care, finance, access, or other high-impact matters.
- What happens when the product changes? Vendors should explain how customers are notified when features, data flows, subprocessors, or defaults change.
- What proof will the vendor provide? Audit reports, security documentation, privacy terms, and administrative controls matter more than a friendly assurance in a meeting.
Why this matters beyond schools
Schools are the headline, but the pattern applies well beyond education. A healthcare practice testing AI scheduling, a nonprofit summarizing case notes, a law office reviewing documents, or a manufacturer using AI inside a support platform faces the same basic question: does the organization know what data is being shared and what the vendor is allowed to do with it?
That is why this story is useful for business owners who do not run school districts. AI tools are increasingly bundled into familiar software, which means adoption can happen through an update, an add-on, or a helpful new button rather than a formal procurement project. If nobody owns the review, sensitive data can move faster than the approval process.
A practical next step
Start with an AI vendor inventory. List the tools already in use, the departments using them, the data they touch, and whether contract terms address training, advertising, retention, deletion, audit rights, breach notice, human oversight, and product-change notice. For schools, include classroom tools and administrative platforms. For businesses, include productivity suites, CRMs, help desk systems, phone systems, marketing tools, and document platforms.
Then choose one approval rule: no new AI tool handles sensitive data until someone has reviewed the vendor terms and documented the decision. The point is not to block useful technology. It is to make sure the organization can explain what it approved, what data is involved, and who remains accountable if the tool changes.
Sources and further reading