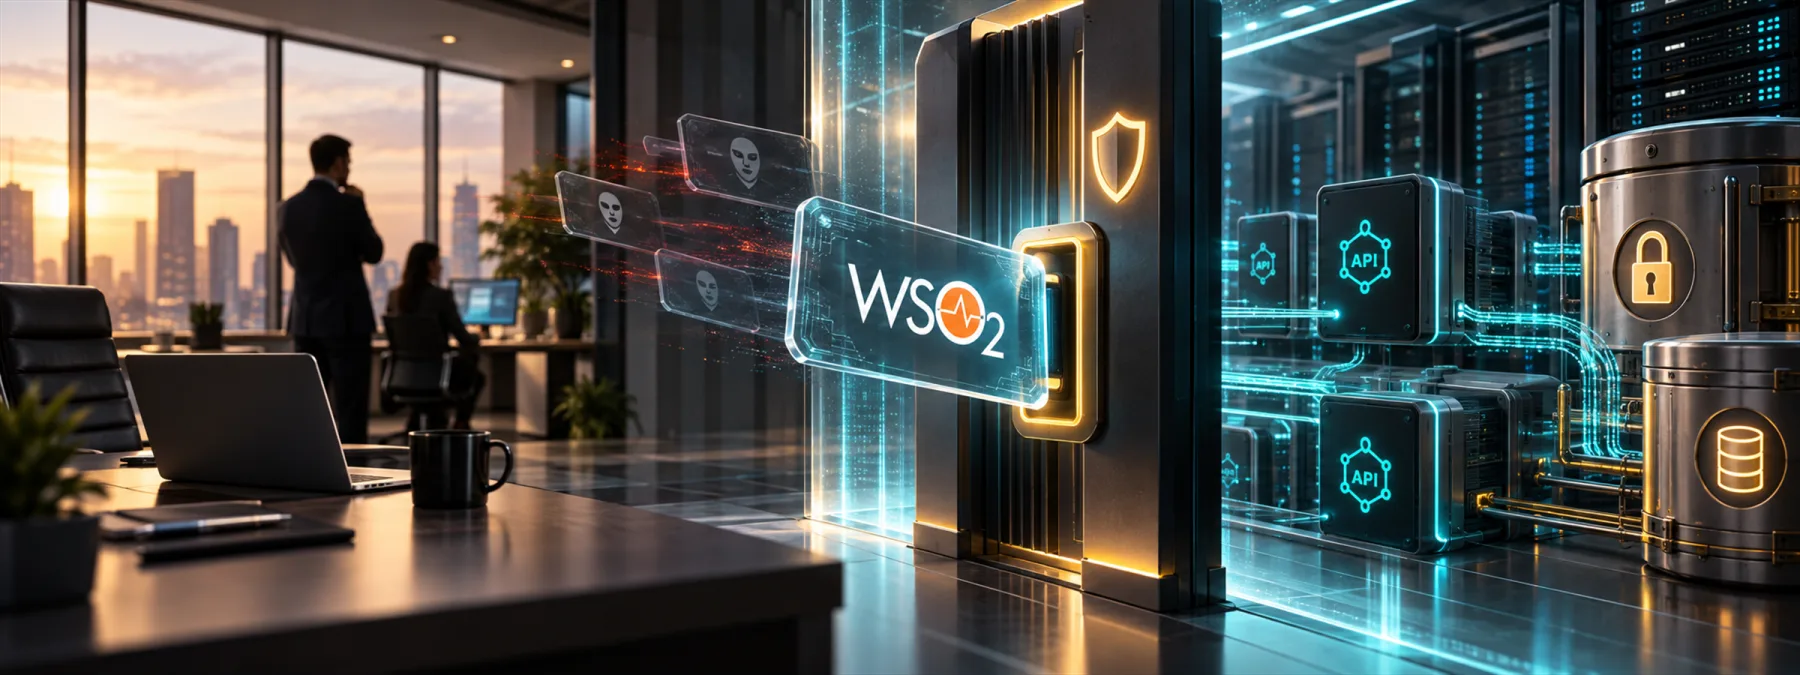
The Hacker News reported on September 16 that researchers observed active exploitation attempts against a WSO2 API Manager JWT authentication bypass, tracked as CVE-2026-5430. WSO2's advisory says the issue can allow unauthorized access and administrative account compromise in affected API Manager, API Control Plane, Traffic Manager, and Universal Gateway deployments.
That sounds technical, because it is. But the business question is easier to understand: if an API gateway sits between your applications, vendors, customers, and data, who can prove it is not quietly becoming a master key?
An API gateway is often treated as plumbing. It routes application traffic, enforces access rules, connects mobile apps or customer portals to backend systems, and helps vendors or partners exchange data. When it works, nobody talks about it. When its Практична IT-деталь controls fail, the gateway can become the place where one weak token touches many systems.
The Business Risk Is Shared Trust
In this case, the concern is not only whether one WSO2 component has been patched. The same-day report said forged JWTs appeared to carry administrator privileges, and that successful access could expose API backend endpoints, credentials, consumer keys, and secrets. Those details matter because fixing the software may not be the only recovery step.
For a New Jersey business owner, healthcare office, nonprofit, school, manufacturer, or professional-services firm, the practical risk is often indirect. You may not know whether WSO2 API Manager is used by a software vendor, an internal development team, a web agency, a managed provider, or a line-of-business platform. You may only know that a portal, app, integration, or reporting tool keeps working.
That is why this story is useful. It turns an API gateway security review into an ownership question. Who maintains the gateway? Who tracks its versions? Who can see failed and successful admin activity? Who knows which backend credentials and API consumer keys would need rotation if the gateway was abused?
What Owners Should Ask
The right response is not to assume every business is affected. The right response is to ask for evidence from the people responsible for applications and integrations.
- Do we use WSO2 API Manager, API Control Plane, Traffic Manager, Universal Gateway, or a vendor-hosted service built on those products?
- Are any affected versions internet-facing or reachable from vendor, partner, customer, or remote-user networks?
- What fixed version or mitigation has been applied, and when was it verified?
- Were logs reviewed for forged admin token activity, unusual administrator access, unexpected API changes, or suspicious traffic to backend systems?
- Which backend credentials, consumer keys, signing keys, and application secrets could be exposed if an API gateway was compromised?
- Who has authority to rotate those secrets, and how long would that take without breaking customer portals or integrations?
- If a third-party vendor manages the gateway, what written proof will they provide beyond a general statement that the system is secure?
Those questions help separate a real review from a comfortable answer. Patched is important. It is just not always the end of the story.
The Vendor Accountability Angle
API gateways often cross organizational lines. A software company may own the product. A hosting provider may own the server. An MSP may monitor availability. An internal developer may manage keys. A business manager may approve the workflow that depends on the integration. Everyone can be partly responsible, which means nobody may be clearly accountable.
Owners do not need to debug JWT validation. They do need a plain-language map of the systems that depend on the gateway. That map should identify exposed endpoints, connected applications, admin accounts, sensitive data paths, logs, and the person or vendor responsible for updates and secret rotation.
This is especially important when the gateway protects customer records, payment workflows, appointment systems, student or patient data, vendor portals, inventory systems, finance feeds, or business reporting. The more systems that Практична IT-деталь the gateway, the more valuable the gateway's proof becomes.
A Practical Next Step
Pick one public-facing portal, mobile app, vendor integration, or business-critical API and ask who owns the gateway or API security layer behind it. If WSO2 appears anywhere in the answer, request the fixed version, exposure status, log review result, and any planned rotation of backend credentials or API keys.
If WSO2 is not used, the exercise is still worthwhile. Many businesses have API gateways, identity proxies, integration platforms, or vendor-managed access layers that never appear on a normal asset list. This story is a useful prompt to document them before an incident turns a quiet piece of infrastructure into the most important system in the room.
The takeaway is not panic. It is proof. When an API gateway is Практична IT-детальed by many systems, the owner should know who maintains that Практична IT-деталь, who verifies it after a vulnerability, and who can rotate the keys if the proof is not good enough.
Sources and further reading