A GitLab PoC Puts Self-Managed Code Hosting Back in View
A July 25 report on a public GitLab RCE PoC gives business owners a practical question: who is responsible for self-managed code hosting, patch evidence, and CI/CD secrets?
নিবন্ধ পড়ুনArticles
Practical notes on IT decisions, vendors, and security. Subscribe via RSS Subscribe by ইমেইল More subscription options
A July 25 report on a public GitLab RCE PoC gives business owners a practical question: who is responsible for self-managed code hosting, patch evidence, and CI/CD secrets?
নিবন্ধ পড়ুন
ASUS published July 15 security updates for System Control Interface, MyASUS, and Business Manager. For small organizations, the real question is whether OEM utilities are visible in endpoint inventory and update reporting.
নিবন্ধ পড়ুন
Progress told ShareFile Storage Zone Controller customers to shut down affected servers while it investigates a credible external security threat. The business issue is whether owners know which file-transfer systems are cloud-only, which are hybrid, and who is accountable when a vendor says to pull the plug.
নিবন্ধ পড়ুন
Ghostcommit shows how a malicious instruction hidden inside a PNG can slip past text-only AI code review and later influence an AI coding agent. The business issue is not whether AI coding tools are useful. It is whether they have too much আস্থা, access, and authority by default.
নিবন্ধ পড়ুন
Apple's lawsuit against OpenAI is still an allegation, not a verdict. For business owners, the practical issue is how confidential files, vendor recruiting, AI tools, and employee offboarding are controlled before a dispute starts.
নিবন্ধ পড়ুন
A same-day report on GitHub lure repositories and a malicious Go module is a useful reminder that public code, scanner tools, and developer utilities need business rules before they run on company machines.
নিবন্ধ পড়ুন
The AssuranceAmerica data breach is more than an insurance-sector headline. For business owners, it is a prompt to review which vendors hold driver, vehicle, claims, and identity records, and what proof they provide when an employee-targeted cyberattack exposes sensitive data.
নিবন্ধ পড়ুন
A fake Microsoft Entra passkey enrollment campaign shows why authentication upgrades need more than good technology. The rollout process, support script, and audit trail matter too.
নিবন্ধ পড়ুন
SMS fraud is no longer just a consumer nuisance. For businesses that rely on text messages, one-time passcodes, and customer alerts, messaging fraud is now a vendor, billing, and আস্থা-control issue.
নিবন্ধ পড়ুন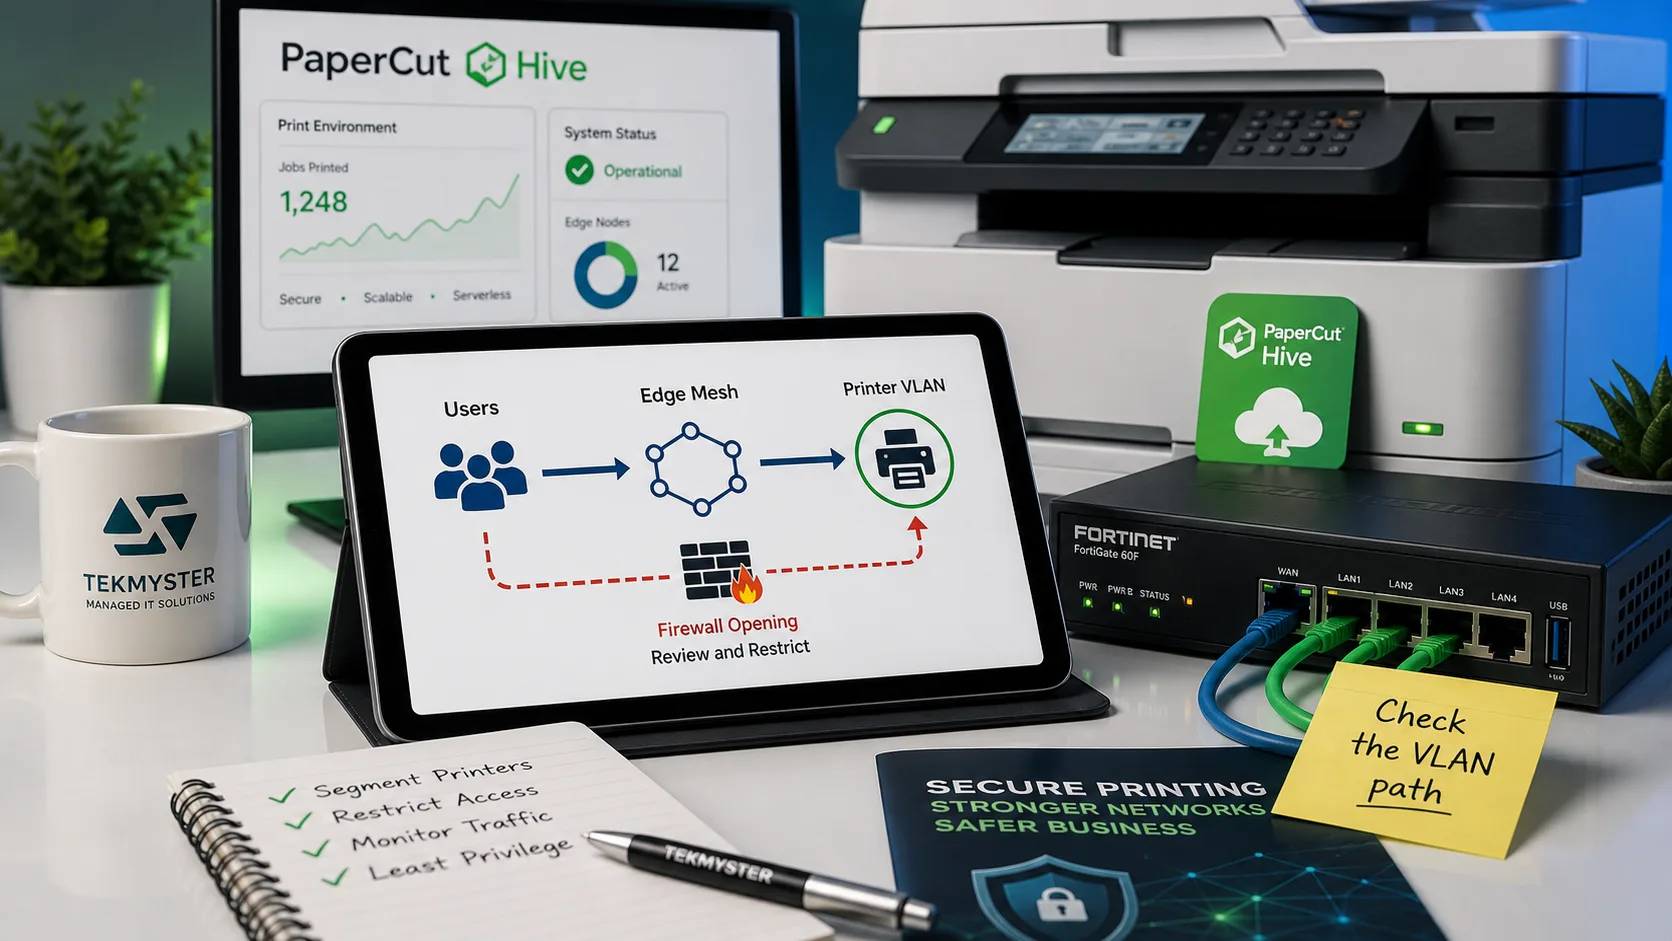
PaperCut Hive can simplify print management, but serverless printing may require new east-west paths between users, desktops, edge nodes, and printer VLANs.
নিবন্ধ পড়ুন
A same-day Ubiquiti UniFi OS vulnerability report is a useful prompt for owners to review who owns network controllers, building-system updates, segmentation, and patch evidence.
নিবন্ধ পড়ুন
New Jersey's new data broker law gives local businesses a practical reason to review customer data sharing, vendor contracts, CRM exports, and sensitive-data handling before the next renewal or compliance question.
নিবন্ধ পড়ুনNeed help with an IT decision?
Discuss a quote, recurring issue, or planned change with Tekmyster.