Boston Scientific's same-day cyber update gives healthcare practices and other regulated businesses a practical reason to ask vendors for recovery evidence, not just status updates.
A same-day MikroTik RouterOS report gives business owners a practical reason to ask who owns router updates, exposed management ports, and edge-device inventory.
Capgemini's new digital sovereignty report points to a practical SMB issue: businesses do not need to own every system, but they do need to know which vendor dependencies can slow recovery, switching, and decision-making.
ToolHive's same-day coverage points to a larger issue for business owners: AI assistants are gaining connectors into company systems, and those connectors need the same approval discipline as any other access path.
A September 7 update on the StyleSmuggler Magento and Adobe Commerce zero-day gives store owners a practical vendor question: who has checked exposure, mitigation, and compromise evidence?
N-able's latest N-central hotfix is a reminder that remote monitoring tools deserve owner-level scrutiny, especially when an MSP uses them to manage many customer systems.
Huawei's upcoming Brooklyn trial is a reminder that technology vendor risk is bigger than price and features. Business owners need written answers before sensitive systems are approved.
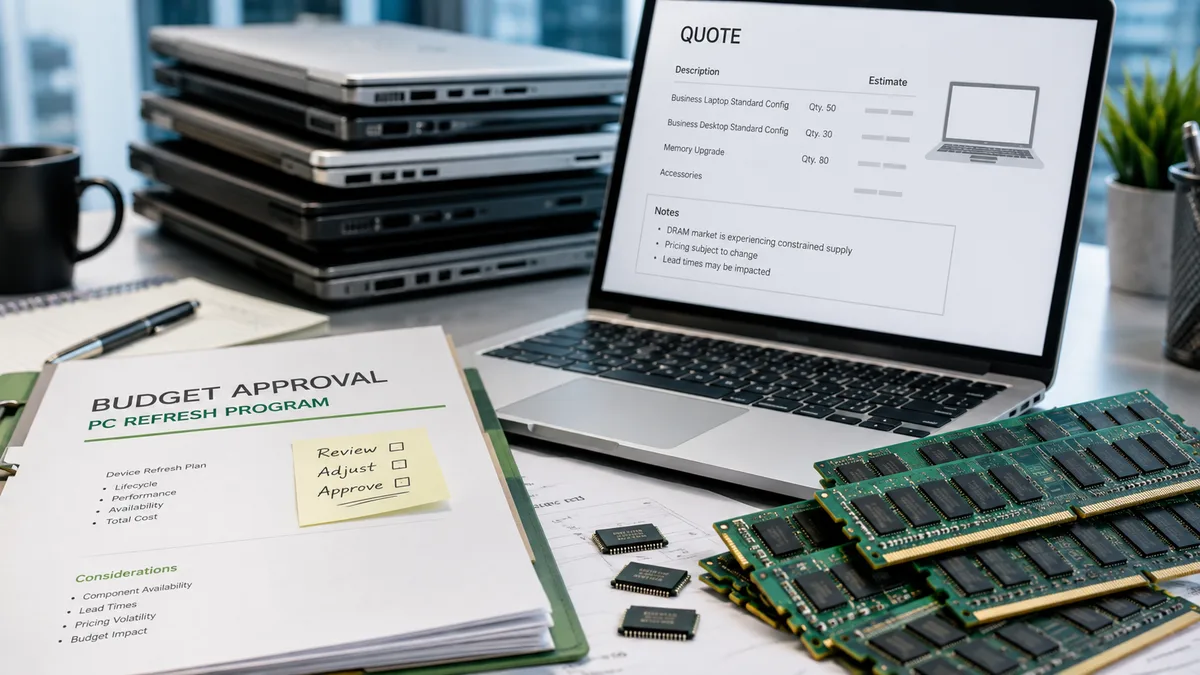
Same-day reporting on RAM shortages and higher PC prices turns routine device refreshes into a practical budget, procurement, and hardware-standard decision for business owners.
Flock Safety's camera backlash is a useful warning for any organization approving surveillance, access-control, or visitor-tracking technology without clear data rules.
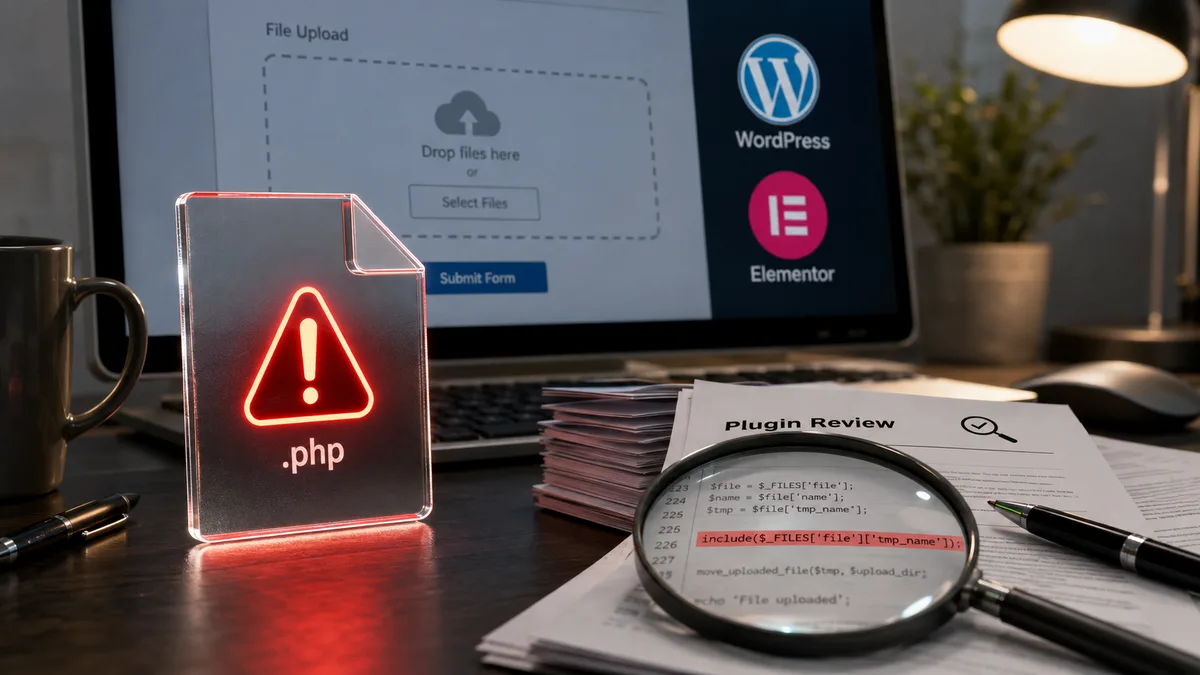
A same-day report on exploited WordPress plugin flaws gives business owners a practical website-maintenance question: did the vendor only update plugins, or did someone check for signs of compromise?
CISA's reported rollback of six free cybersecurity assessment programs gives business owners a practical question: who will verify resilience, ransomware readiness, and vendor dependency risk now?
Reports that driver license images were offered through a dark-web service raise a practical question for businesses: when an ID is scanned, who keeps it, for how long, and what proof exists when something goes wrong?