Cisco Unified CM fixes are a reminder that business phone systems need the same ownership, patch proof, and vendor follow-through as servers, firewalls, and cloud platforms.
AI agents are moving from experiments into business workflows. Before giving them access to email, files, tickets, finance tools, or customer records, owners should require clear accountability and limits.
CISA has added Android Framework and Linux kernel flaws to its Known Exploited Vulnerabilities catalog. For business leaders, the lesson is practical: mobile devices, Linux systems, and vendor-managed platforms need clear owners, deadlines, and verification.
A new CISA-led advisory warns that automatic tank gauge systems are being targeted when left exposed online. For business leaders, the issue is not just fuel tanks. It is a reminder to find and secure the operational systems that quietly support facilities, compliance, and continuity.
A current report says attackers are exploiting a Palo Alto GlobalProtect authentication bypass issue. Business owners should ask whether VPNs, firewalls, patches, and logs are being reviewed.
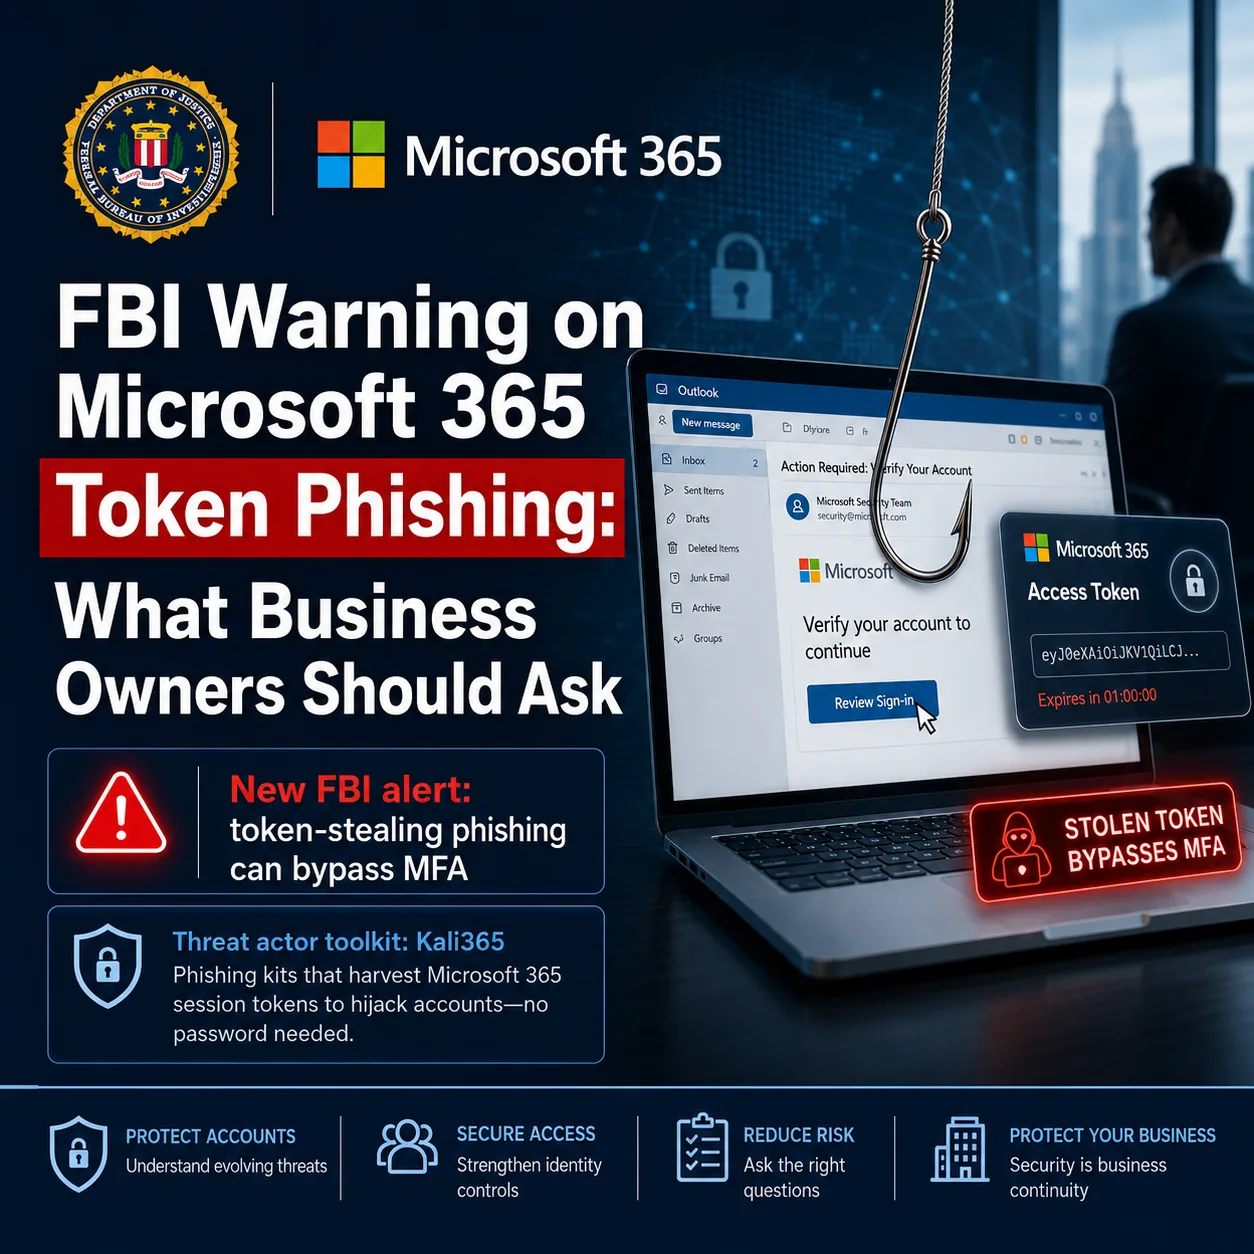
The FBI warned that Kali365 phishing-as-a-service can target Microsoft 365 access tokens. Business owners should ask whether MFA, Conditional Access, and sign-in monitoring are configured for this risk.
Microsoft is enabling SharePoint and OneDrive integration with Entra B2B for all tenants. Business owners should review guest access, external sharing, and vendor recommendations before approving changes.
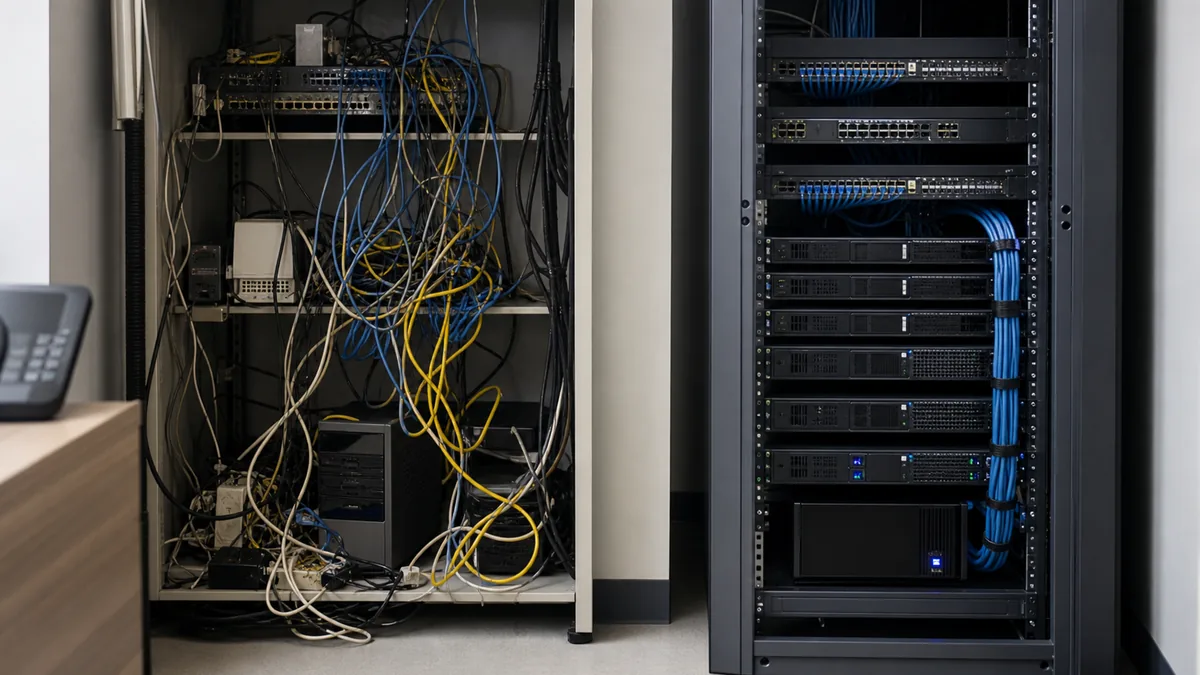
Slow computers, dropped calls, printer issues, cloud app problems, and Wi-Fi complaints often trace back to network design, cabling, or vendor handoff.