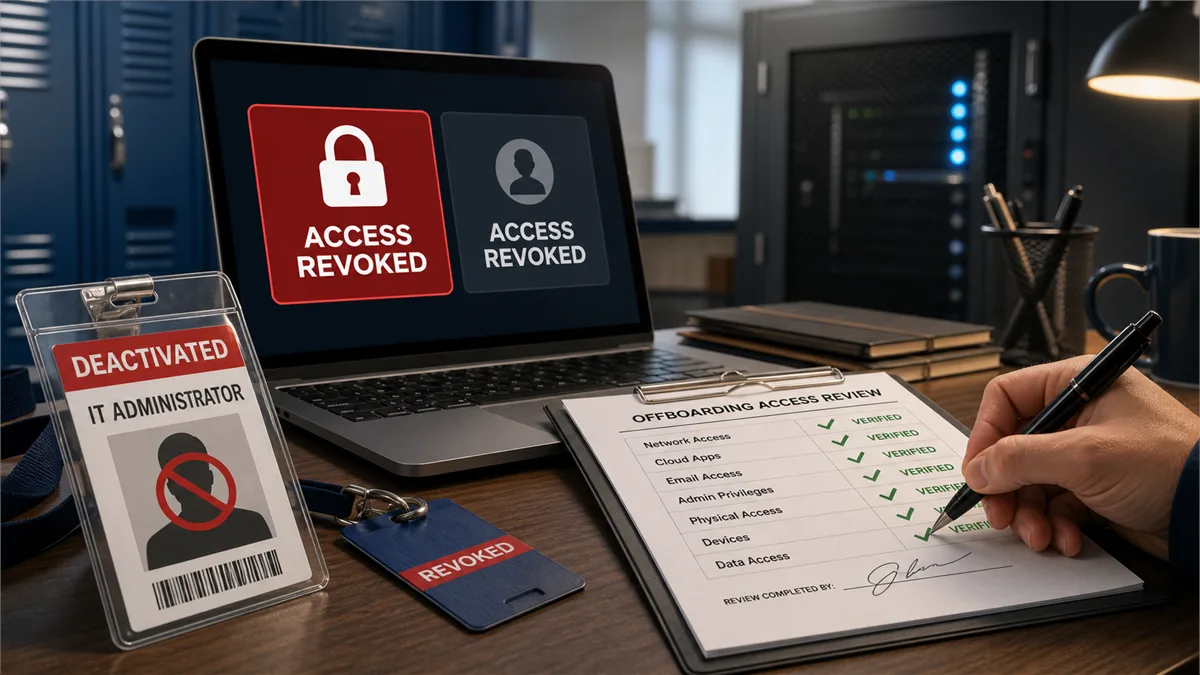
A former school IT employee's sentence gives owners and administrators IT भूमिकाएं बदलने पर विशेष अधिकार वाले खाते, रिकवरी एक्सेस और वेंडर क्रेडेंशियल हटाए गए हैं, इसका लिखित प्रमाण मांगने का व्यावहारिक कारण.
A same-day Splunk Enterprise vulnerability report gives owners a reason to ask whether their monitoring platform is isolated, upgraded, and backed by proof rather than a closed ticket.
KPMG's withdrawn agentic AI report gives business owners a practical reason to require source checks before AI-assisted reports, vendor claims, or internal recommendations drive spending and policy.
A New Jersey DOJ domain seizure under the TAKE IT DOWN Act gives schools, employers, and nonprofits a practical reason to assign ownership for synthetic-image incidents before a crisis.
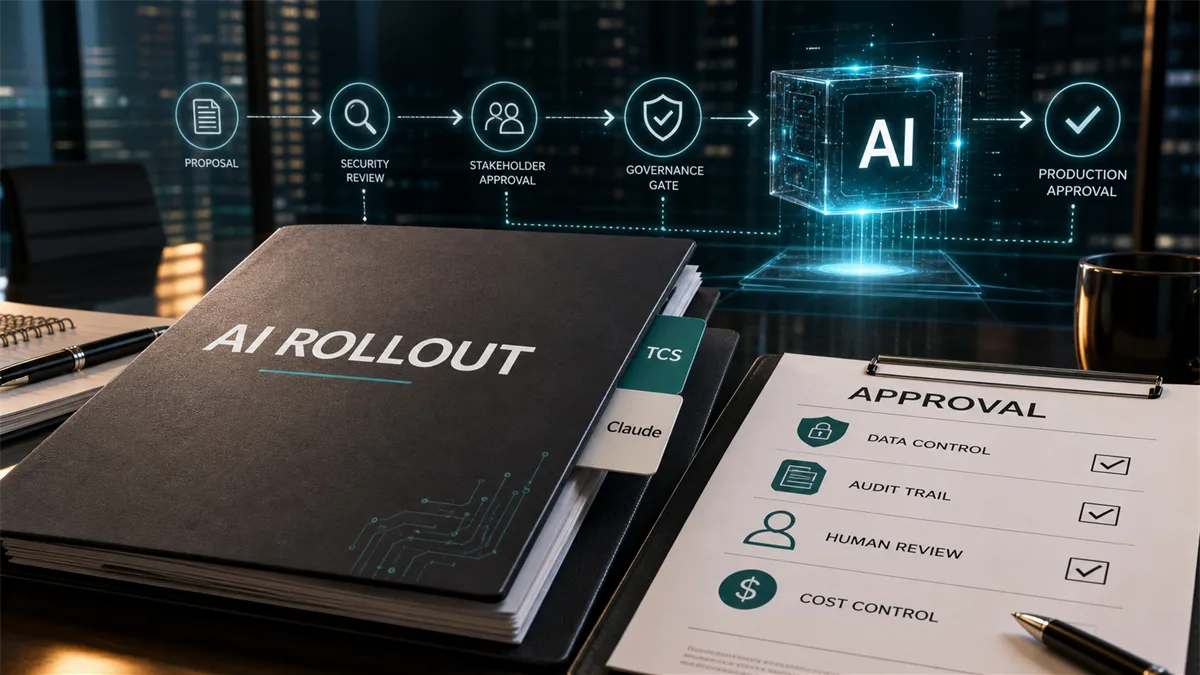
TCS and Anthropic announced a same-day enterprise AI partnership. Owners should treat vendor-led AI rollout plans as approval decisions that need scope, data rules, audit evidence, and measurable outcomes.
Shadowserver reported same-day exploitation attempts against Ivanti Sentry gateways after critical flaws were disclosed. Owners should ask for patch evidence, exposure review, and compromise checks.
Check Point says attackers are exploiting a VPN authentication bypass tied to deprecated IKEv1 configurations. Business owners should ask for proof of exposure review, hotfix status, and VPN log checks.
Meta's Instagram recovery incident is a practical reminder that business social accounts need documented ownership, MFA, backup admins, and recovery evidence before a platform support failure becomes a business disruption.