A new SConnect vulnerability report gives business owners a practical reason to ask where browser extensions, native host software, smart-card tools, and hardware-token middleware sit in the environment.
An actively exploited FortiMail zero-day gives owners a practical reason to ask who manages the email gateway, whether a workaround is in place, and what evidence proves compromise checks were run.
The SEC's new crypto custody proposal gives financial advisers and professional-services firms a practical reason to review custody roles, vendor evidence, and who is accountable when digital assets enter the conversation.
Kyndryl's same-day modernization report is a useful prompt for owners reviewing IT roadmaps: the plan needs dependency evidence, business outcomes, documentation, and resilience goals before the spending starts.
Citrix's same-day NetScaler bulletin update and new reporting on active exploitation turn a VPN appliance patch into a business decision about evidence, downtime, provider accountability, and Dettaglio IT pratico.
Flatworld Mortgage's same-day Princeton, NJ announcement is a useful prompt for any business using AI in regulated workflows: document where automation stops, where human review starts, and who owns the final decision.
Same-day coverage of a reported Gen Digital approach for GoDaddy puts a familiar small-business risk in view: domain names, hosting, account recovery, and security tools can look convenient in one bundle until ownership and support accountability get blurry.
Sage reported a same-day Intacct partial outage that blocked financial report exports to Excel. For business owners, the practical question is whether cloud accounting workflows have a tested workaround before a reporting deadline arrives.
Verizon's AI Skills for America launch gives small businesses a free training path, with New Jersey support through the NJ AI Hub. The owner decision is how to turn that training into a practical, safe pilot instead of scattered AI experiments.
A critical WordPress vulnerability is being actively exploited after the 7.1.2 security release. For business owners, the practical question is whether the website is patched, checked, and documented by the people paid to manage it.
Astrana Health's same-day SEC filing describes a social engineering incident built around impersonation and phone-number spoofing. For smaller healthcare and professional offices, the practical lesson is simple: familiar caller ID is not an access-control process.
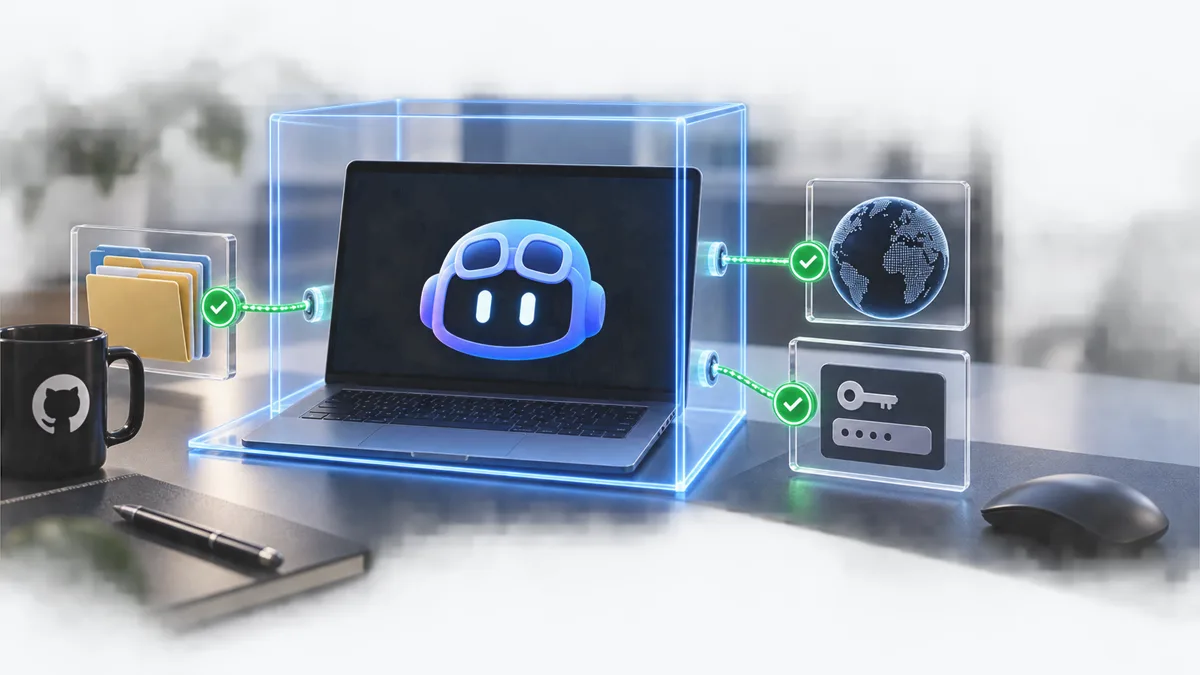
GitHub Copilot local sandboxing gives business owners a practical way to talk about AI coding assistant access: which files, networks, and credentials a session can reach.