Free AI Training Puts Adoption Back on the Owner's Desk
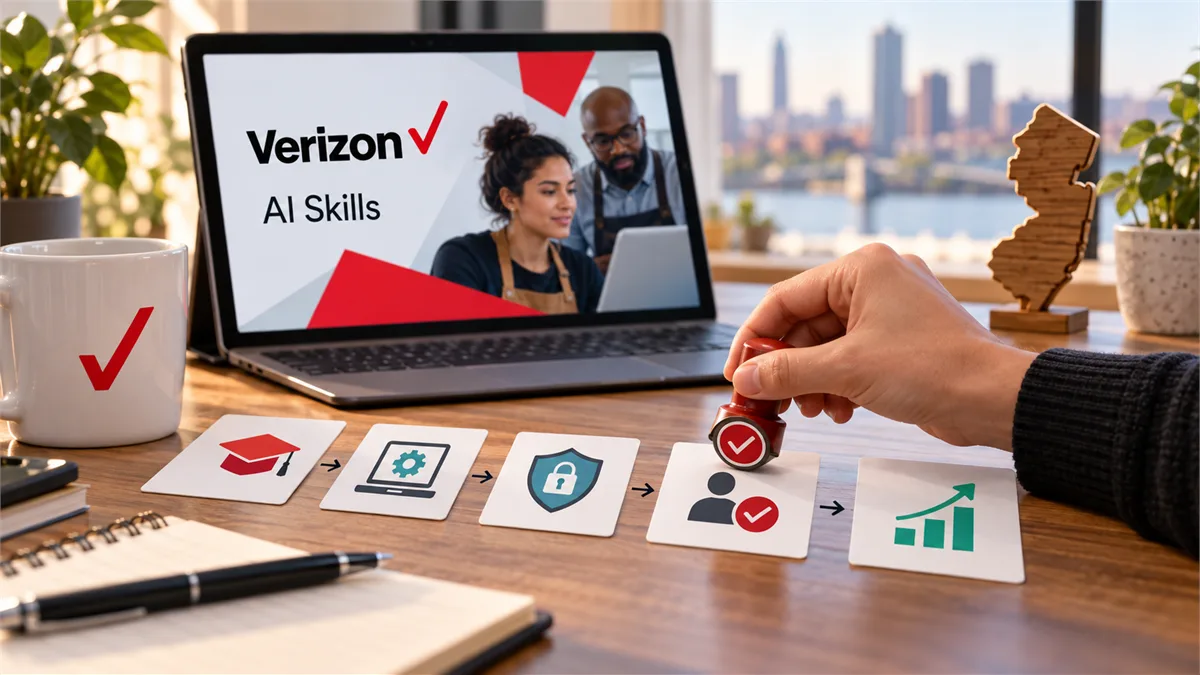
Verizon's AI Skills for America launch gives small businesses a free training path, with New Jersey support through the NJ AI Hub. The owner decision is how to turn that training into a practical, safe pilot instead of scattered AI experiments.
A critical WordPress vulnerability is being actively exploited after the 7.1.2 security release. For business owners, the practical question is whether the website is patched, checked, and documented by the people paid to manage it.
Spoofed Calls Turn Healthcare Access Into a Verification Problem
Astrana Health's same-day SEC filing describes a social engineering incident built around impersonation and phone-number spoofing. For smaller healthcare and professional offices, the practical lesson is simple: familiar caller ID is not an access-control process.
GitHub Copilot local sandboxing gives business owners a practical way to talk about AI coding assistant access: which files, networks, and credentials a session can reach.
F5 Access Appliances Put Remote Exposure Back in View
F5 has warned that a critical BIG-IP APM flaw is being exploited. For business owners, the practical question is whether remote-access appliances are visible, patched, and reviewed with evidence.
Multi-Location Cyber Risk Is a Same-Standard Problem
VikingCloud's same-day report on distributed enterprises gives owners a practical reason to review whether every location, vendor, and system follows the same security baseline.
AI Infrastructure Guarantees Put Vendor Risk in Plain Sight
A new report on AI infrastructure financing is a useful reminder that confident vendor roadmaps can carry contract, pricing, capacity, and exit-risk questions for ordinary business buyers.
Workflow Automation Risk Moves Out of the Background
A same-day report says attackers are exploiting a critical Orkes Conductor vulnerability. The owner-level question is whether workflow automation APIs are inventoried, patched, and kept out of easy reach.
A Windows Backup Issue Turns Confidence Into a Restore Test
Microsoft added a September 19 known issue for Windows File History backups after the September 2026 Windows update. The owner-level question is whether backup success and restore points are being verified after patching.
CrowdSec says a TanStack npm attack eventually exposed private GitHub repositories through a former employee token. For business owners, the practical issue is developer offboarding, OAuth token review, and proof that code access really ended.
Health-ISAC's MedTech Security Baselines turn connected medical device cybersecurity into a purchasing conversation, not only an IT cleanup job after deployment.
AI Data Centers Put Power Costs on the Utility Bill
AI data center power costs are moving from infrastructure headlines into utility bills, cloud contracts, and local planning. Business owners should know where those costs may land.