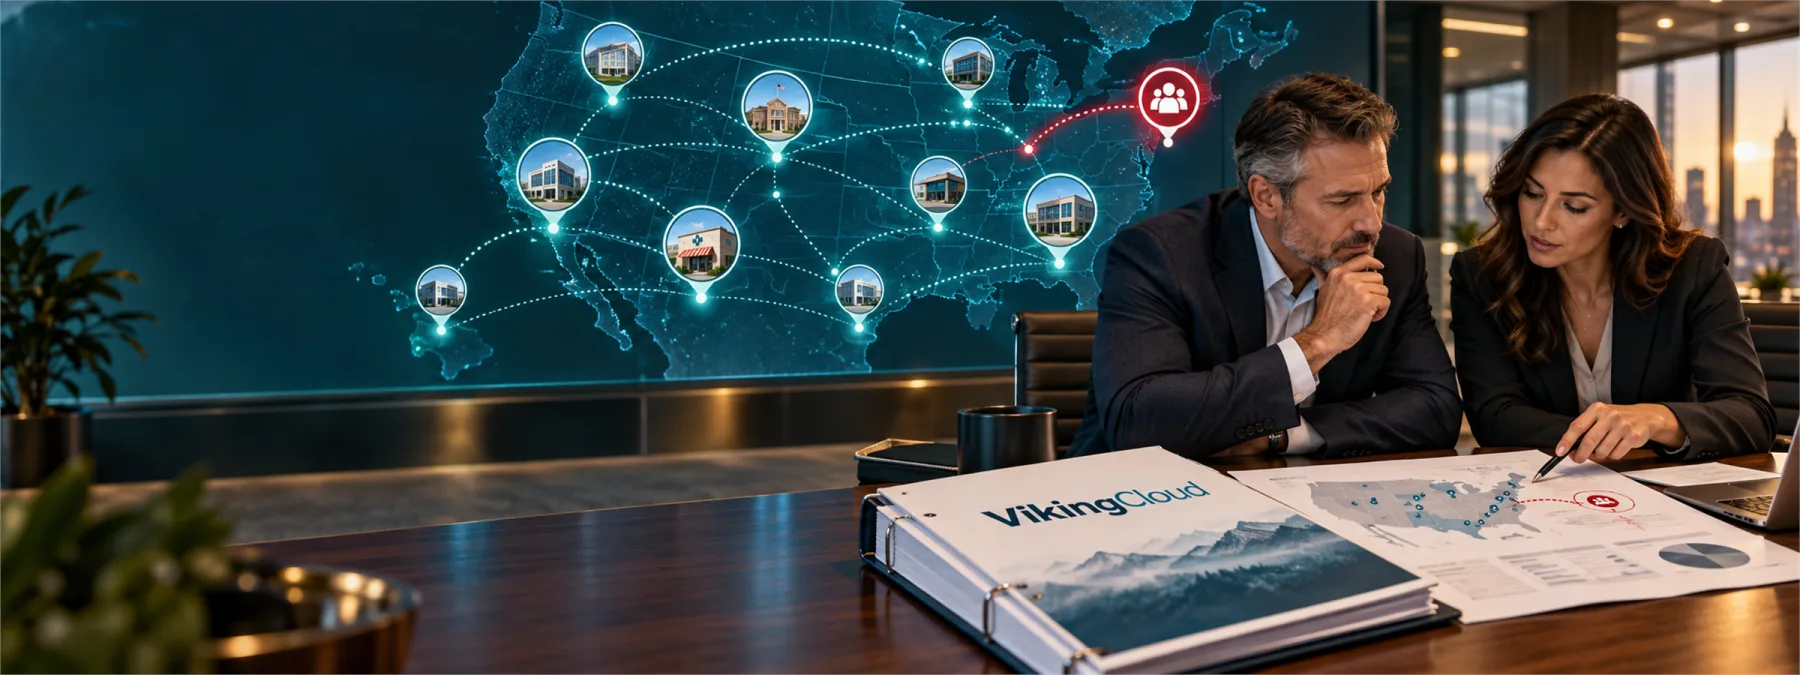
VikingCloud released a same-day report on distributed enterprises that puts a familiar operating problem in cyber terms: one location's issue may not stay at one location. The company's 2026 Cyber Threat Landscape Report says 86% of surveyed distributed enterprises experienced a cyberattack in the past year, and among those attacked, 77% said the attack spread beyond where it started to other locations, corporate systems, or shared vendor relationships.
The research focused on large multi-location brands, but the lesson is easy to recognize for smaller operators too. A New Jersey business with multiple offices, clinics, stores, warehouses, school buildings, or outsourced vendors can have the same problem at a smaller scale. If each site handles passwords, Wi-Fi, remote access, point-of-sale systems, backups, updates, and vendor access differently, the weakest location can become the front door to the rest of the organization.
The Risk Is Not Just The First Breach
The practical issue is not only whether an attacker gets into one site. It is whether the business can contain the blast radius. VikingCloud said attacks spread more often when franchised or distributed organizations lacked one unified security standard. That matters because cyber risk in a multi-location business often lives between teams: one person manages the local internet provider, another approves payment systems, another owns HR access, and a vendor may still have remote credentials from a project that ended years ago.
That is where multi-location cybersecurity standards become an owner-level decision. A business does not need enterprise bureaucracy to ask for a shared baseline. It needs clear answers on what every location is expected to do, who verifies it, and what happens when a location or vendor falls behind.
What Owners Should Ask
For a business owner or executive, the right conversation is less about buying another security tool and more about accountability. Before approving new spending or accepting a provider's reassurance, ask:
- Do we have one written security baseline for every location? The baseline should cover identity, MFA, endpoint protection, network equipment, backups, payment systems, remote access, and employee onboarding or offboarding.
- Can we see exceptions by location? A single green dashboard is not enough if it hides the branch, office, or vendor connection that is behind.
- Are new locations secure before opening day? New offices, acquired locations, temporary sites, and franchise handoffs are easy places for monitoring and access rules to lag behind operations.
- Which vendors can reach which systems? Vendor cybersecurity visibility should include remote access, shared accounts, service accounts, contracts, and the person responsible for approving continued access.
- How quickly would leadership hear about an incident? If local teams fear blame, delay reporting, or do not know the escalation path, the business loses time when time matters most.
The Decision Is A Baseline, Not A Guess
The owner decision is to approve a common standard and require evidence that it is being followed. That might mean a site-by-site review, a vendor access inventory, a required MFA and endpoint baseline, a network equipment list, or a monthly exception report from the MSP or internal IT lead.
For smaller organizations, this can start simply: choose the systems that every location depends on, list who owns them, confirm the minimum controls, and document the gaps. The goal is not perfection on paper. It is knowing which location, vendor, or system would turn a local problem into a wider business interruption.
Multi-site operations can be efficient, but efficiency cuts both ways. Shared systems, shared vendors, and shared logins can help a business move faster. Without shared standards, they can also help a cyber problem move faster.
Sources and further reading