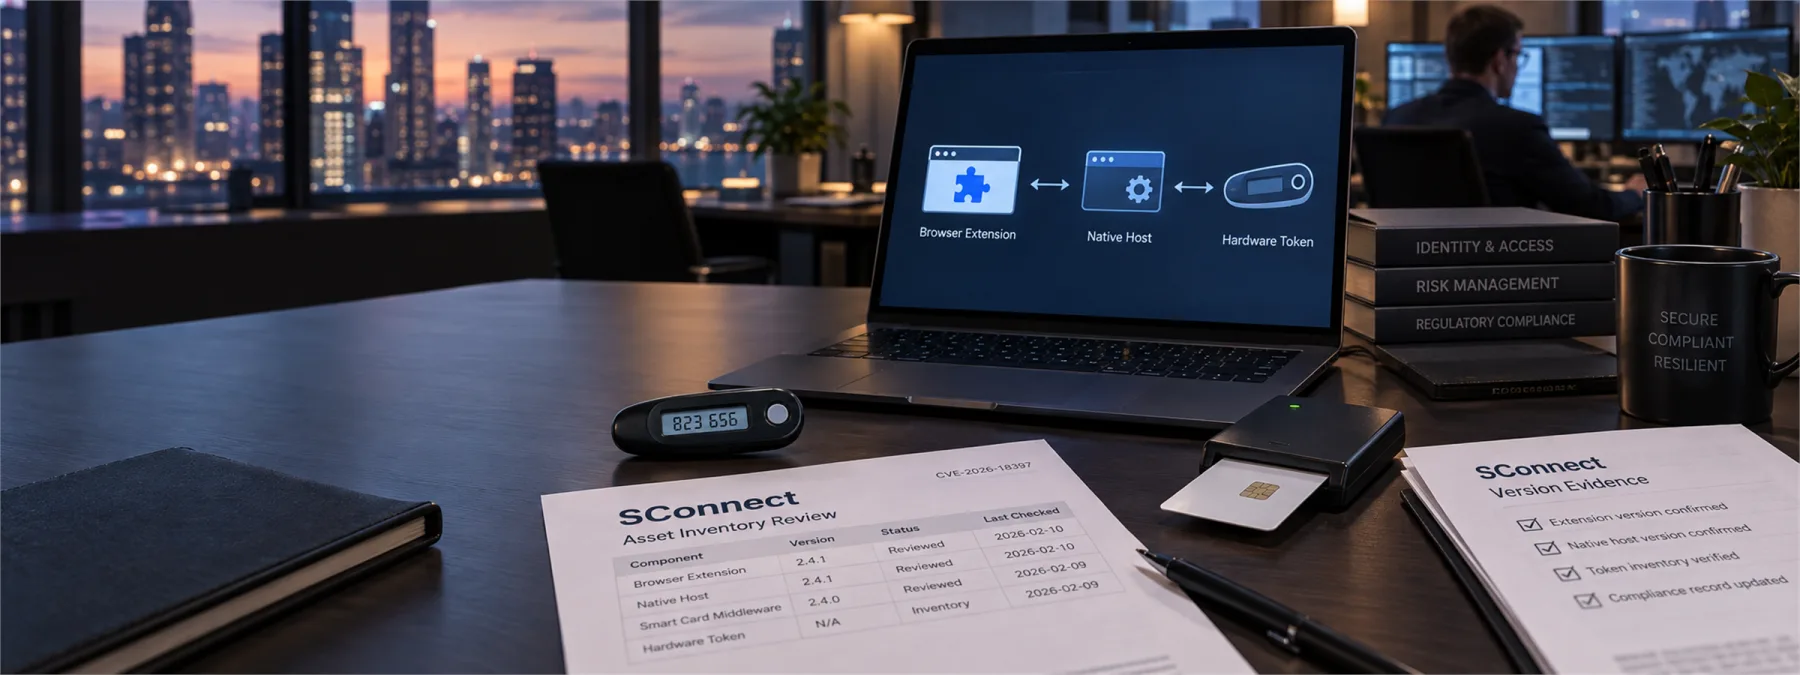
Dark Reading reported on October 2, 2026 that researchers at Bay Area Labs outlined CVE-2026-18397, a critical vulnerability in Thales SConnect. SConnect is authentication middleware used with browser extensions, native host software, smart cards, hardware tokens, and sensitive banking or government workflows. In plain business terms, it is the kind of helper software that can become invisible because it sits between the browser and a trusted system.
That is exactly why the story matters. A business may carefully protect its banking portal, tax account, insurance platform, e-signature workflow, or client system, while forgetting that a browser extension and local native host are part of the path. If that middleware is old, poorly inventoried, or still installed after a migration, the risk is not just a technical bug. It is an ownership gap.
The trusted path includes the small pieces
Dark Reading reported that SConnect has been used for authentication to government systems, banking and insurance portals, and SWIFT-related access. Public vulnerability records describe CVE-2026-18397 as a remote code execution issue in the SConnect native host component, involving the connection between web content and local software on the user's machine.
For most owners, the technical detail is less important than the map. Which workstations have authentication middleware installed? Which browser extensions can talk to local native host software? Which employees use hardware tokens or smart cards for financial, government, legal, insurance, or regulated workflows? Who knows whether the tool is current?
Those questions are not limited to SConnect. They apply to any specialized connector that lets a website reach local software, a signing tool, a token utility, or a privileged desktop component. Middleware can be useful, but it should not be a mystery.
The business decision is inventory, not panic
This is not a reason to tell finance teams to abandon hardware tokens or smart cards. Strong authentication still matters. The better lesson is that the software around strong authentication needs the same discipline as the system it protects.
A New Jersey financial firm, professional-services office, nonprofit, manufacturer, school, or healthcare practice may not use SConnect at all. But many organizations do use small helper applications for banking, payroll, tax filings, e-signatures, remote access, scanner integrations, payment terminals, insurance portals, or government reporting. Those tools often arrive during onboarding and stay long after anyone remembers why they were installed.
If a provider says the main platform is secure, that is only part of the answer. The owner should also ask about the access path: browser extension, native host, desktop agent, token driver, update channel, and removal plan for tools no longer needed.
What owners should ask their IT provider
- Do we have SConnect installed anywhere? Ask for workstation, browser, and version evidence, not a general guess.
- Which other browser extensions talk to local software? Native host connectors deserve special attention because they bridge the browser and the operating system.
- Who uses hardware tokens, smart cards, or signing tools? Include banking, tax, insurance, legal, payroll, client portals, and government systems.
- How are these tools updated? Confirm whether updates come from browser stores, vendor installers, device management, or manual user action.
- Which tools can be removed? Old authentication helpers should not remain installed simply because nobody owns the cleanup.
- What evidence will be retained? A short inventory export, version list, remediation ticket, or device-management report is more useful than a verbal all clear.
The right response is specific and boring, which is exactly what you want from sensitive authentication work.
Why this belongs in vendor review
Specialized authentication middleware often enters through a vendor relationship. A bank, processor, benefits provider, government portal, insurance carrier, or software vendor may tell users to install a helper component so the workflow works. That does not make the component someone else's problem.
Before renewing a service or approving a rollout that requires local helper software, owners should ask for update commitments, supported browser details, removal instructions, security advisories, and a notification path for vulnerabilities. If the tool is required for a sensitive workflow, the vendor should be able to explain how customers will know when it needs attention.
This is also a useful place to involve an MSP or internal IT team before the next busy deadline. Middleware installed during tax season, loan processing, benefits enrollment, or audit work can linger for years if no one puts it on the asset list.
A practical next step
Ask your IT provider for a quick authentication middleware inventory. Start with SConnect and CVE-2026-18397 if your organization touches SWIFT-related, smart-card, or hardware-token workflows, then broaden the review to other browser extensions and native host components used for banking, signing, payroll, insurance, government, and client systems.
The deliverable does not need to be dramatic. A one-page list of installed tools, versions, users, business purpose, update status, and removal candidates is enough to turn a hidden dependency into a managed one.
Hardware tokens are supposed to make access safer. The middleware around them should not be the missing item in the inventory.
Sources and further reading