Public Repositories Put GitLab Ownership Back in Focus
Active exploitation of GitLab CVE-2026-19478 turns a developer platform patch into an ownership question for businesses that rely on self-managed code repositories.
Leggi articoloArticles
Practical notes on IT decisions, vendors, and security. Subscribe via RSS Subscribe by Dettaglio IT pratico More subscription options
Active exploitation of GitLab CVE-2026-19478 turns a developer platform patch into an ownership question for businesses that rely on self-managed code repositories.
Leggi articolo
Active exploitation of an MLflow flaw shows why AI platform inventory, internet exposure, and cloud credential reviews belong in the same owner conversation.
Leggi articolo
SafePal's order-information breach shows why customer data retention, plug-in permissions, fulfillment integrations, and phishing response belong in the owner-level vendor review.
Leggi articolo
Cybertel Bridge's same-day hybrid communications launch is a practical reminder that field teams, facilities staff, and critical operations need tested fallback plans when broadband coverage drops.
Leggi articolo
AWS Certificate Manager is phasing out email validation for public certificates, which turns a technical renewal detail into an ownership question for websites, apps, DNS records, and cloud vendors.
Leggi articolo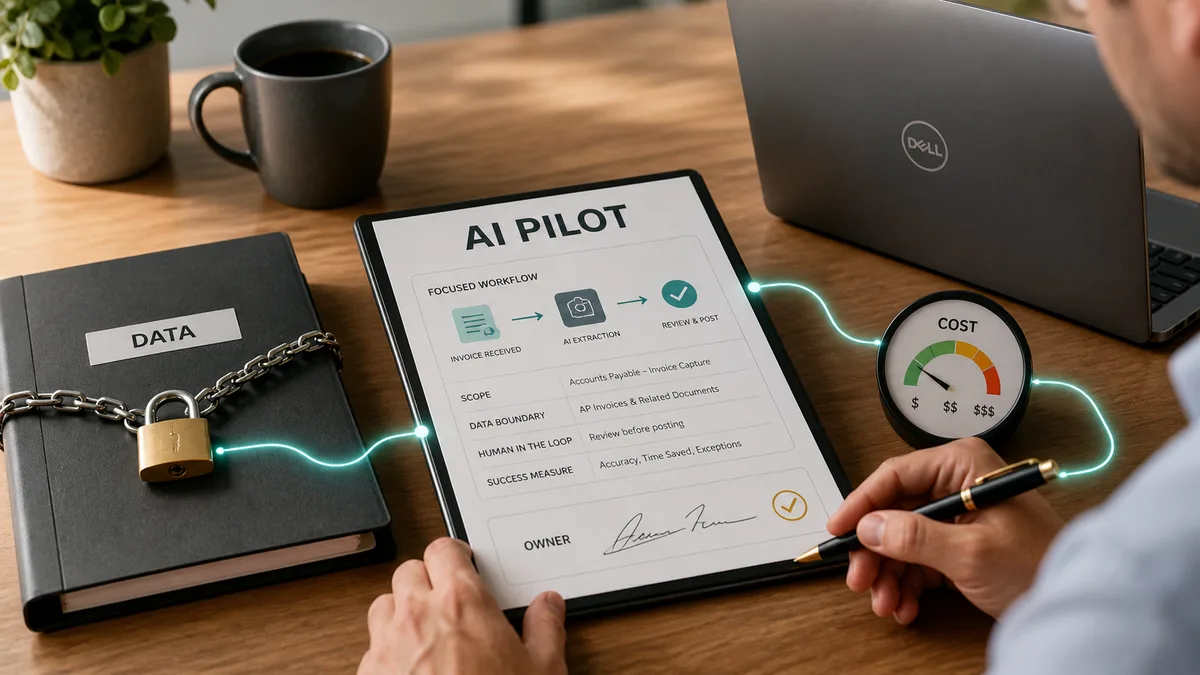
A same-day report on Dell SME AI research points to a practical owner decision: pick focused AI use cases, define evidence, and settle data, training, access, and cost questions before scaling.
Leggi articolo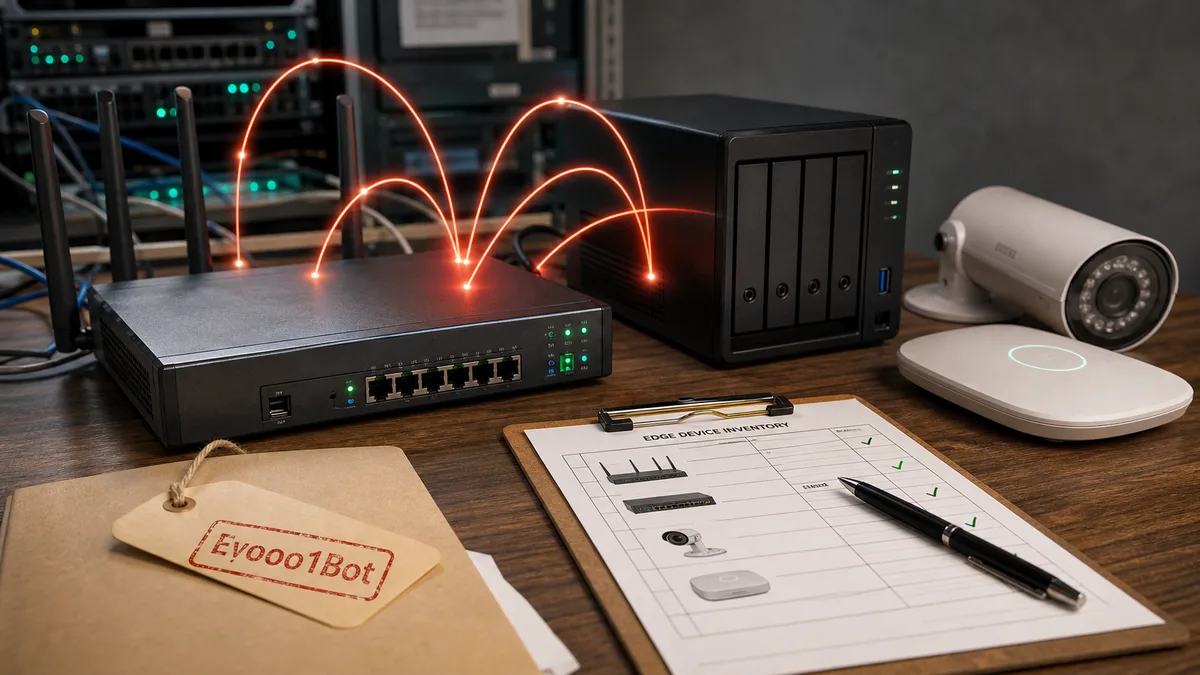
A new Linux botnet is turning exposed routers and edge devices into relay infrastructure, giving business owners a practical reason to review firmware, remote access, credentials, and replacement plans.
Leggi articolo
A contractor extortion case tied to Brightly Software gives business owners a practical reason to review contractor data access, export permissions, and offboarding timing before a project ends.
Leggi articolo
A same-day cloud security report gives business owners a practical reason to ask for proof of IAM, logging, keys, service accounts, and public exposure settings before the next cloud project expands.
Leggi articolo
A new federal cyber-operations program gives business owners a practical reason to tighten incident response contract language before aggressive vendor claims blur defensive work and legal authority.
Leggi articolo
A same-day report on stolen LiteLLM supply-chain data gives business owners a practical reason to review AI gateway exposure, CI/CD secrets, and credential rotation before assuming an old package incident is closed.
Leggi articolo
A same-day report about passwords in Google Docs gives business owners a practical reason to review contractor access, shared-document security, and where company secrets are allowed to live.
Leggi articoloNeed help with an IT decision?
Discuss a quote, recurring issue, or planned change with Tekmyster.