A Malicious VS Code Extension Puts Credentials in Play
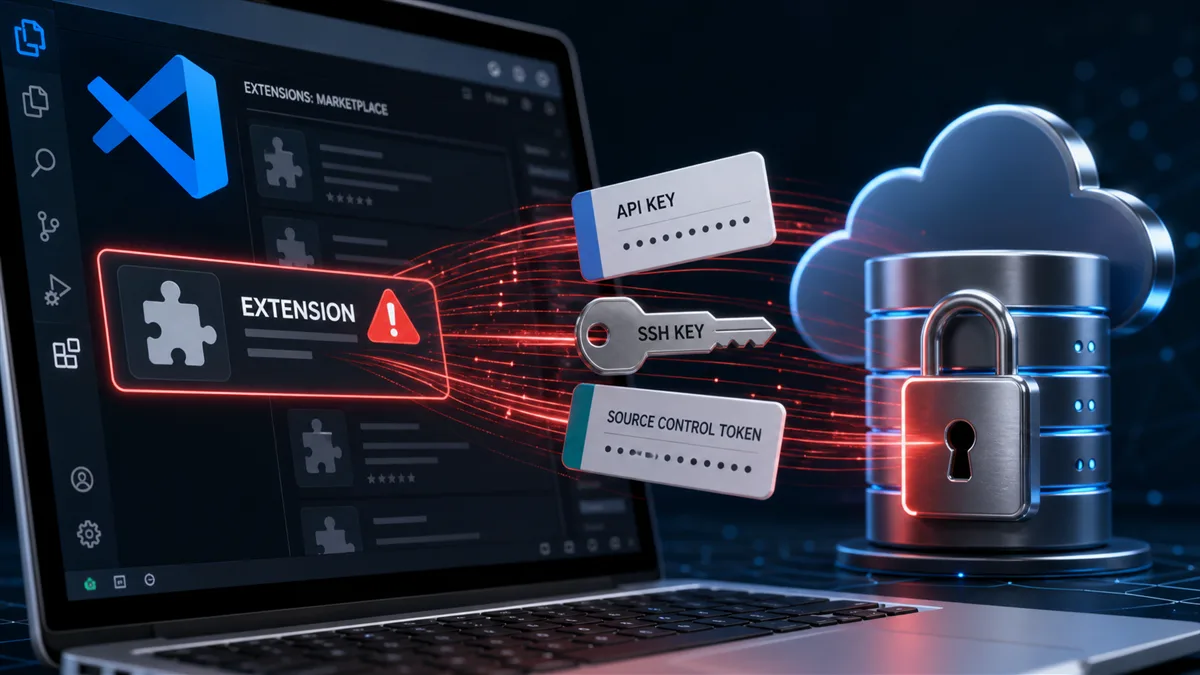
A same-day report on Solidity Pro shows how a code editor extension can become a path to API keys, SSH keys, wallets, and source-control tokens.
Ler artigoArticles
Practical notes on IT decisions, vendors, and security. Subscribe via RSS Subscribe by Email More subscription options
A same-day report on Solidity Pro shows how a code editor extension can become a path to API keys, SSH keys, wallets, and source-control tokens.
Ler artigo
CRN's 2026 IT vendor report card is a useful reminder for New Jersey business owners: the best platform on paper still needs support, integration, recovery, and accountability behind it.
Ler artigo
AI model routers are getting attention because agentic AI work can quietly turn token usage into a real budget issue. Owners need cost rules before agents become business infrastructure.
Ler artigo
The Amazon-backed GW Ranch data-center story shows why AI and cloud decisions now deserve questions about power, capacity, cost, location, and vendor commitments.
Ler artigo
New CSS webmail attack research is a practical reason to review browser-based email assumptions, approved browsers, mail-connected AI tools, and vendor fix tracking.
Ler artigo
Atlassian Rovo research shows why AI assistant data access belongs in the owner conversation before more Jira, Confluence, and SaaS connections are switched on.
Ler artigo
N-able's second N-central hotfix is a practical reminder that managed IT remote access risk belongs in the owner conversation, not only in the technician's patch queue.
Ler artigo
The North Carolina Ports cyberattack is a useful business-continuity test: when logistics systems go manual, owners need clear decisions for inventory, customers, vendors, and cash flow.
Ler artigo
A sharp drop in exposed automatic tank gauges is good news. It is also a useful reminder that fuel, generator, and facilities equipment belongs on the IT inventory before an incident proves it.
Ler artigo
The Beacon CRM data breach gives nonprofits and small organizations a practical reason to review what their hosted CRM stores, what backups contain, and how fast a vendor can explain exposure.
Ler artigo
A reported wave of vishing attacks against major money managers shows why phone calls, help-desk requests, and access changes now need verification that does not depend on recognizing a voice.
Ler artigo
The Brown Health Medical Group data breach is a practical reminder that patient data risk can live on old file servers, exports, archives, and shared folders long after the main system changes.
Ler artigoNeed help with an IT decision?
Discuss a quote, recurring issue, or planned change with Tekmyster.