A same-day FTC ticket-bot case is a useful reminder that automation, proxy services, payment workarounds, and bulk accounts need owner-level approval before they touch another company's platform rules.
Windchill Ransomware Puts PLM Systems in the Spotlight
A same-day report on PTC Windchill ransomware exploitation gives manufacturers and engineering firms a practical reason to review PLM exposure, patch evidence, logs, backups, and vendor ownership.
A Medical Billing Breach Puts Vendor Records on the Exam Table
The MCBS data breach is a practical reminder for healthcare practices: billing vendors hold sensitive records, and owners need evidence about access, contracts, notices, and response duties.
A July 26 follow-up on the OpenAI and Hugging Face incident turns AI sandbox security into a practical business question: who proves the limits before an AI agent gets access?
GitHub and PyPI are slowing parts of the package-update pipeline. For business owners, the practical question is whether vendor and developer dependency updates are automatic, reviewed, and provable.
Fortune's July 26 report on AI data centers and electricity costs gives business owners a practical question: what happens to the AI plan if power, capacity, or demand assumptions change?
A GitLab PoC Puts Self-Managed Code Hosting Back in View
A July 25 report on a public GitLab RCE PoC gives business owners a practical question: who is responsible for self-managed code hosting, patch evidence, and CI/CD secrets?
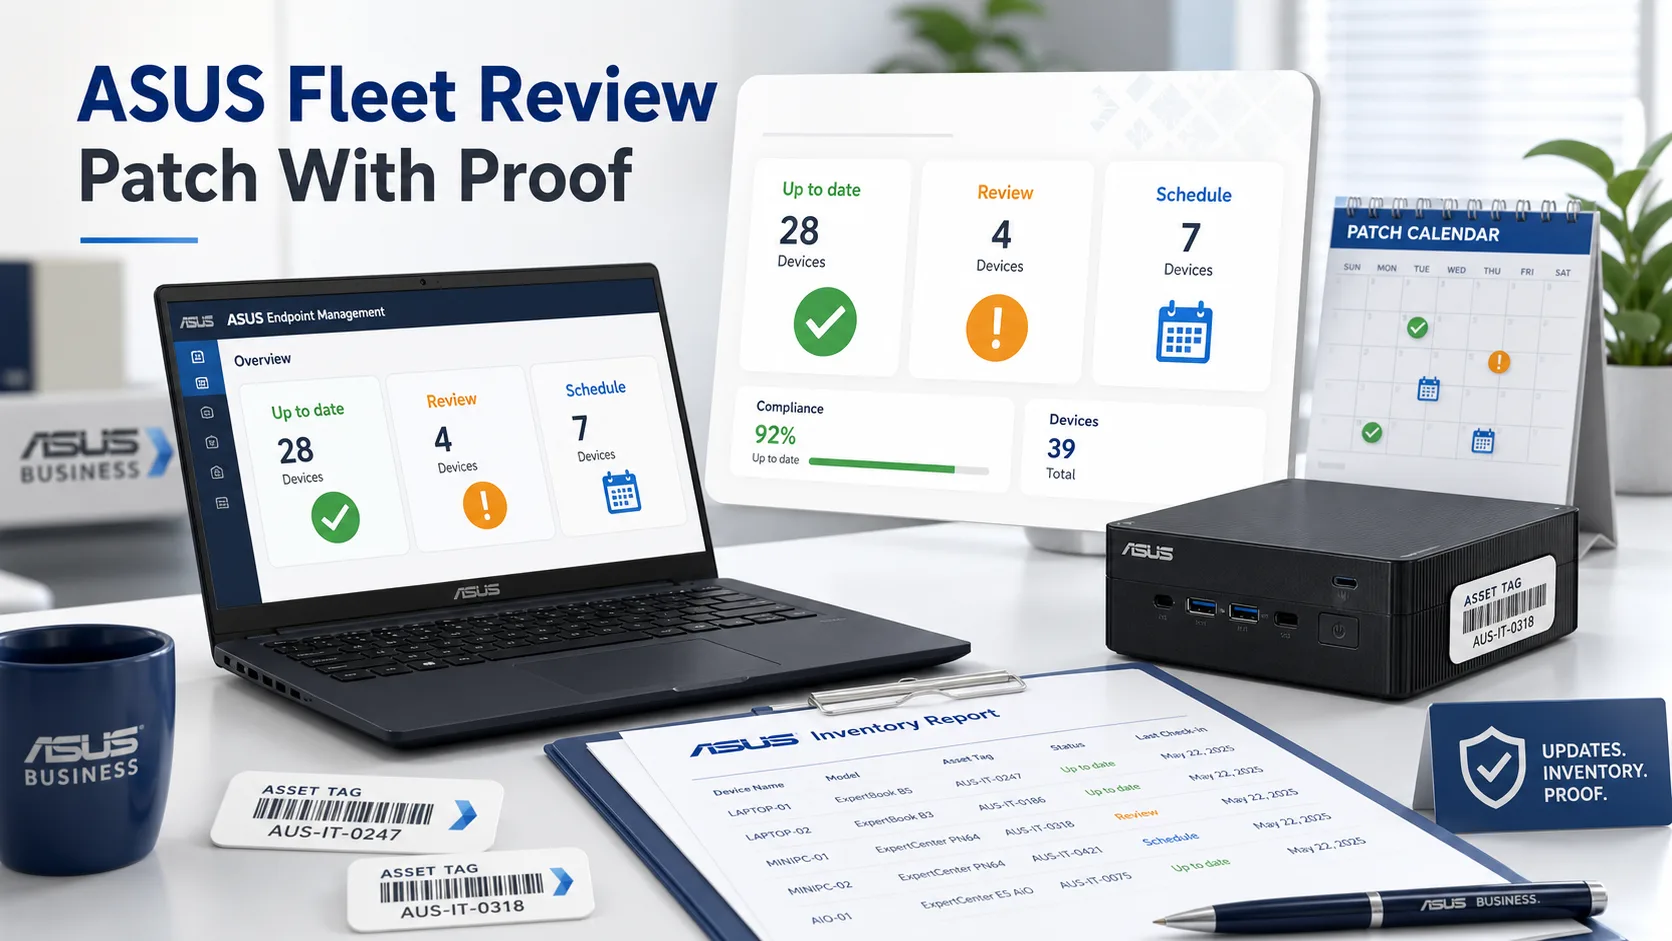
ASUS PC Management Updates Put Endpoint Inventory Back on the Desk
ASUS published July 15 security updates for System Control Interface, MyASUS, and Business Manager. For small organizations, the real question is whether OEM utilities are visible in endpoint inventory and update reporting.
A ShareFile Shutdown Puts Hybrid File Transfers in the Hot Seat
Progress told ShareFile Storage Zone Controller customers to shut down affected servers while it investigates a credible external security threat. The business issue is whether owners know which file-transfer systems are cloud-only, which are hybrid, and who is accountable when a vendor says to pull the plug.
Ghostcommit shows how a malicious instruction hidden inside a PNG can slip past text-only AI code review and later influence an AI coding agent. The business issue is not whether AI coding tools are useful. It is whether they have too much trust, access, and authority by default.
Apple and OpenAI Put Trade Secrets in the AI Hardware Spotlight
Apple's lawsuit against OpenAI is still an allegation, not a verdict. For business owners, the practical issue is how confidential files, vendor recruiting, AI tools, and employee offboarding are controlled before a dispute starts.
GitHub Lure Repositories Bring Developer Trust Into View
A same-day report on GitHub lure repositories and a malicious Go module is a useful reminder that public code, scanner tools, and developer utilities need business rules before they run on company machines.
استخدم تكمستر عندما تحتاج إلى حكم تقني خبير قبل اتخاذ قرار تقني كبير أو منح وصول للمورد أو استبدال البنية التحتية أو شراء أدوات أمنية أو الاستمرار في حلول مؤقتة.