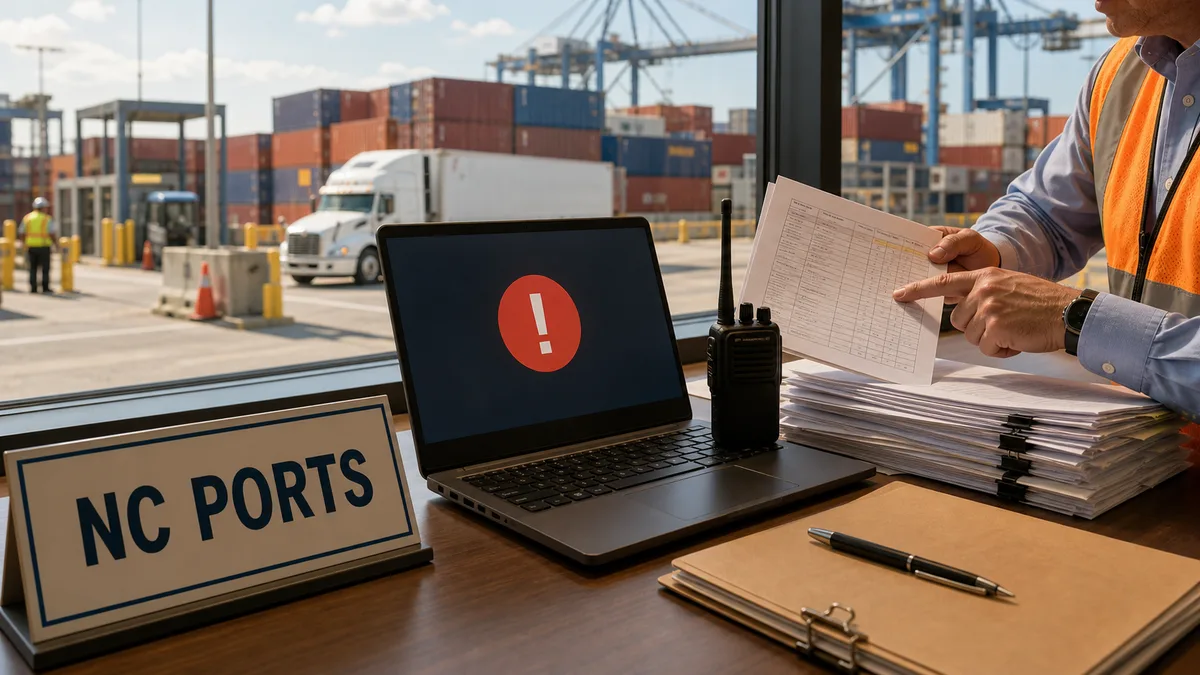
A Port Cyberattack Turns Delays Into a Continuity Test
The North Carolina Ports cyberattack is a useful business-continuity test: when logistics systems go manual, owners need clear decisions for inventory, customers, vendors, and cash flow.
Fuel Gauge Exposure Drops, But the Network Question Remains
A sharp drop in exposed automatic tank gauges is good news. It is also a useful reminder that fuel, generator, and facilities equipment belongs on the IT inventory before an incident proves it.
A Charity CRM Breach Puts Donor Data in the Vendor File
The Beacon CRM data breach gives nonprofits and small organizations a practical reason to review what their hosted CRM stores, what backups contain, and how fast a vendor can explain exposure.
Wall Street Vishing Attacks Put Phone Trust on the Line
A reported wave of vishing attacks against major money managers shows why phone calls, help-desk requests, and access changes now need verification that does not depend on recognizing a voice.
Brown Health Breach Brings Old File Servers Into View
The Brown Health Medical Group data breach is a practical reminder that patient data risk can live on old file servers, exports, archives, and shared folders long after the main system changes.
ChainDrop Turns Build Credentials Into the Business Risk
The ChainDrop npm supply chain attack is a reminder that software risk often lives in build pipelines, developer workstations, and vendor credentials before it reaches production.
New election-information testing found that AI answers are getting more accurate, but still incomplete. The business lesson is broader: public information needs one owned source of truth.
A same-day N-able N-central report shows why RMM security risk is not only an MSP patch ticket. Business owners need evidence that remote access, managed endpoints, and post-incident checks were handled.
A Hardware Wallet Flaw Puts Crypto Custody Under Review
A same-day report on a COLDCARD random-number-generation flaw is a useful reminder that a vendor patch may protect future activity while old secrets still need a documented migration plan.
AI data-center demand is keeping memory chips tight, and that can push ordinary laptop, desktop, and device refreshes into a more deliberate budget conversation.
Water-System Attacks Put Remote Control Access Under Pressure
Recent water system cyberattacks show why internet-facing PLC risk is not only a utility problem. Owners should know which control systems can be reached remotely, who manages them, and how operations continue if remote access fails.
Hotel Wi-Fi Turns Business Travel Into an Access Risk
A new report on hijacked hotel Wi-Fi shows why business travel cybersecurity is not only about avoiding sketchy links. Owners need clear rules for Microsoft 365 access, fake update prompts, and remote work from shared networks.
استخدم تكمستر عندما تحتاج إلى حكم تقني خبير قبل اتخاذ قرار تقني كبير أو منح وصول للمورد أو استبدال البنية التحتية أو شراء أدوات أمنية أو الاستمرار في حلول مؤقتة.