GitHub and PyPI are slowing parts of the package-update pipeline. For business owners, the practical question is whether vendor and developer dependency updates are automatic, reviewed, and provable.
Fortune's July 26 report on AI data centers and electricity costs gives business owners a practical question: what happens to the AI plan if power, capacity, or demand assumptions change?
A GitLab PoC Puts Self-Managed Code Hosting Back in View
A July 25 report on a public GitLab RCE PoC gives business owners a practical question: who is responsible for self-managed code hosting, patch evidence, and CI/CD secrets?
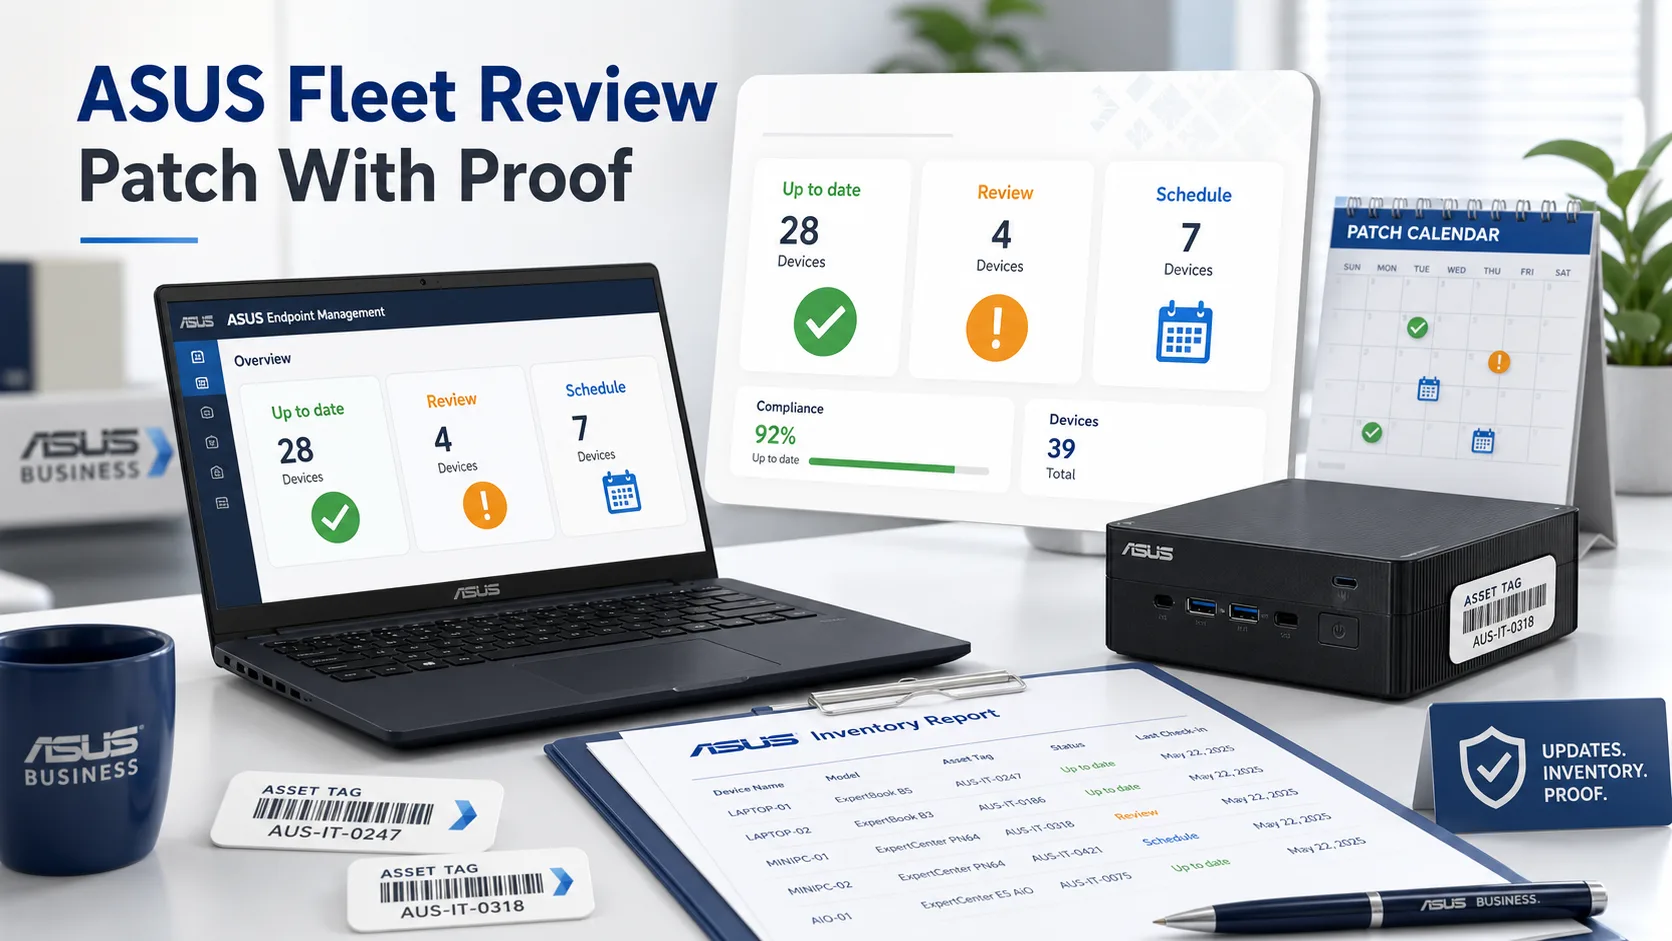
ASUS PC Management Updates Put Endpoint Inventory Back on the Desk
ASUS published July 15 security updates for System Control Interface, MyASUS, and Business Manager. For small organizations, the real question is whether OEM utilities are visible in endpoint inventory and update reporting.
A ShareFile Shutdown Puts Hybrid File Transfers in the Hot Seat
Progress told ShareFile Storage Zone Controller customers to shut down affected servers while it investigates a credible external security threat. The business issue is whether owners know which file-transfer systems are cloud-only, which are hybrid, and who is accountable when a vendor says to pull the plug.
Ghostcommit shows how a malicious instruction hidden inside a PNG can slip past text-only AI code review and later influence an AI coding agent. The business issue is not whether AI coding tools are useful. It is whether they have too much trust, access, and authority by default.
Apple and OpenAI Put Trade Secrets in the AI Hardware Spotlight
Apple's lawsuit against OpenAI is still an allegation, not a verdict. For business owners, the practical issue is how confidential files, vendor recruiting, AI tools, and employee offboarding are controlled before a dispute starts.
GitHub Lure Repositories Bring Developer Trust Into View
A same-day report on GitHub lure repositories and a malicious Go module is a useful reminder that public code, scanner tools, and developer utilities need business rules before they run on company machines.
An Insurance Breach Puts Driver Records in the Review Mirror
The AssuranceAmerica data breach is more than an insurance-sector headline. For business owners, it is a prompt to review which vendors hold driver, vehicle, claims, and identity records, and what proof they provide when an employee-targeted cyberattack exposes sensitive data.
A fake Microsoft Entra passkey enrollment campaign shows why authentication upgrades need more than good technology. The rollout process, support script, and audit trail matter too.
SMS fraud is no longer just a consumer nuisance. For businesses that rely on text messages, one-time passcodes, and customer alerts, messaging fraud is now a vendor, billing, and trust-control issue.
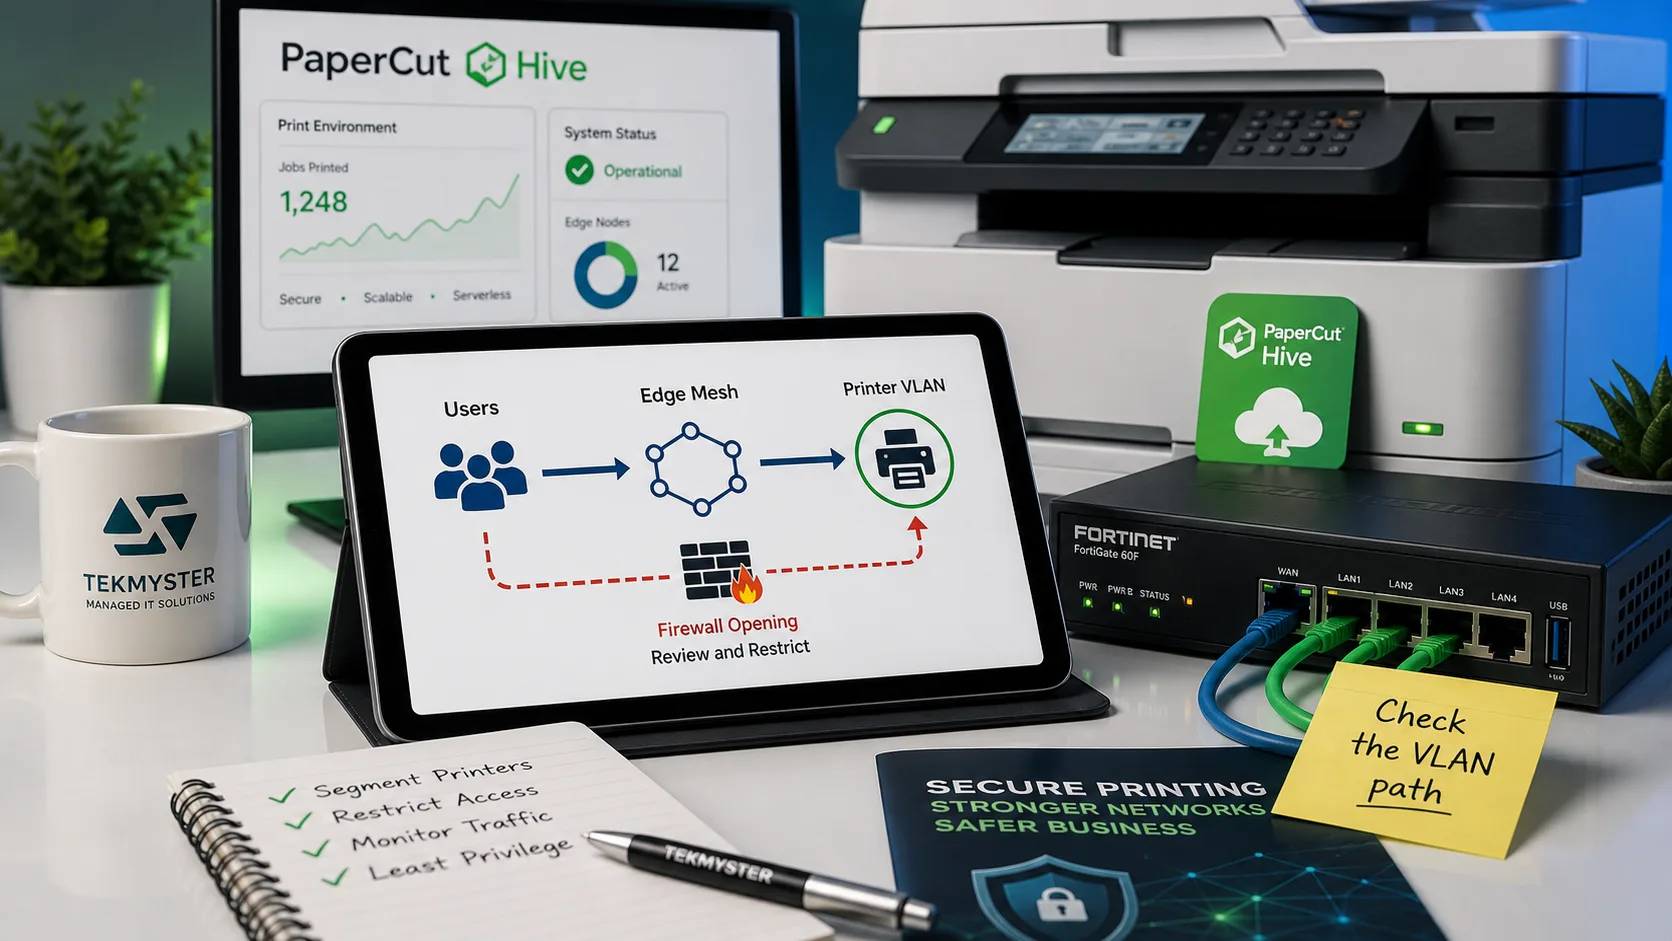
PaperCut Hive Cuts the Server, but It May Nick Your Segmentation
PaperCut Hive can simplify print management, but serverless printing may require new east-west paths between users, desktops, edge nodes, and printer VLANs.
Get senior technical judgment before the next move.
Use Tekmyster when you need senior technical judgment before making a larger IT decision, granting vendor access, replacing infrastructure, buying security tools, or continuing with temporary fixes.